Security by design means that security is not added retroactively but integrated into the architecture of industrial IoT solutions from the very start. This is especially critical in the Industrial IoT, because here it is not only data that must be protected: the processes through which data controls plants and operations must also be considered and safeguarded from the outset.
An IoT System House that takes security by design seriously treats security as an integral part of design, implementation, and operation. The result is an architecture that is not only functional but also resilient, transparent, and auditable.
Why security is especially important in the Industrial IoT
Industrial IoT connects physical assets with digital systems. This creates entirely new, complex attack vectors and therefore new risks as well. As soon as sensors, controllers, platforms, and interfaces are networked, the importance of cybersecurity increases considerably.
More connectivity, more attack surface
The more processes are digitalized, the more components have to be secured. This concerns not only access to platforms but also the connected devices at the endpoints, their data collection and transmission, their interfaces, and the associated operational processes, including how they are maintained.
Security incidents have operational consequences
In industrial environments, cyber incidents are not directed at IT alone. All relevant information points must be secured, because a cyber incident can disrupt operational workflows, corrupt data, or even impair plant availability. That is why cybersecurity in the IoT domain is always a matter of operational safety as well.
Security is a factor of trust
Companies looking to deploy IoT solutions expect transparent protection mechanisms. Security is therefore not only a technical requirement but also an organizational one, making it an important criterion for trust and approval.
What security by design means in concrete terms
Security by design means that security requirements must be taken into account starting as early as the planning phase. The architecture must be fundamentally built so that protection, control, and traceability are integrated from the beginning.
Protection on multiple levels
A secure IoT architecture addresses several levels:
- end devices and sensors,
- communication and networks,
- platform and applications,
- access and permissions,
- operation and monitoring
- organizational processes
Security is not achieved through a single tool but through the coordinated interplay of technical and organizational levels.
Security requirements as an architectural principle
Security is not just an add-on. It influences how systems are segmented, how data is transmitted, and how roles and access rights are organized. That is why security requirements must be considered early in the project.
Traceability and auditability
Industrial companies often require documented processes, clear responsibilities, and traceable decisions. Security by design supports exactly that, because security measures are embedded in the architecture and operation from the outset.
The building blocks of a secure IoT architecture
A resilient IoT security architecture consists of several interlocking components.
Segmentation
Not all systems should be directly connected to one another. Segmentation helps create security zones and makes movement within the network controllable. This is especially important in mixed IT/OT environments.
Access control
Only authorized people and systems may access IoT components. This includes role models, authentication, permission management, and logging.
Encryption
Data must be protected both in transit and at rest. Encryption is a key measure for ensuring confidentiality and integrity.
Monitoring and logging
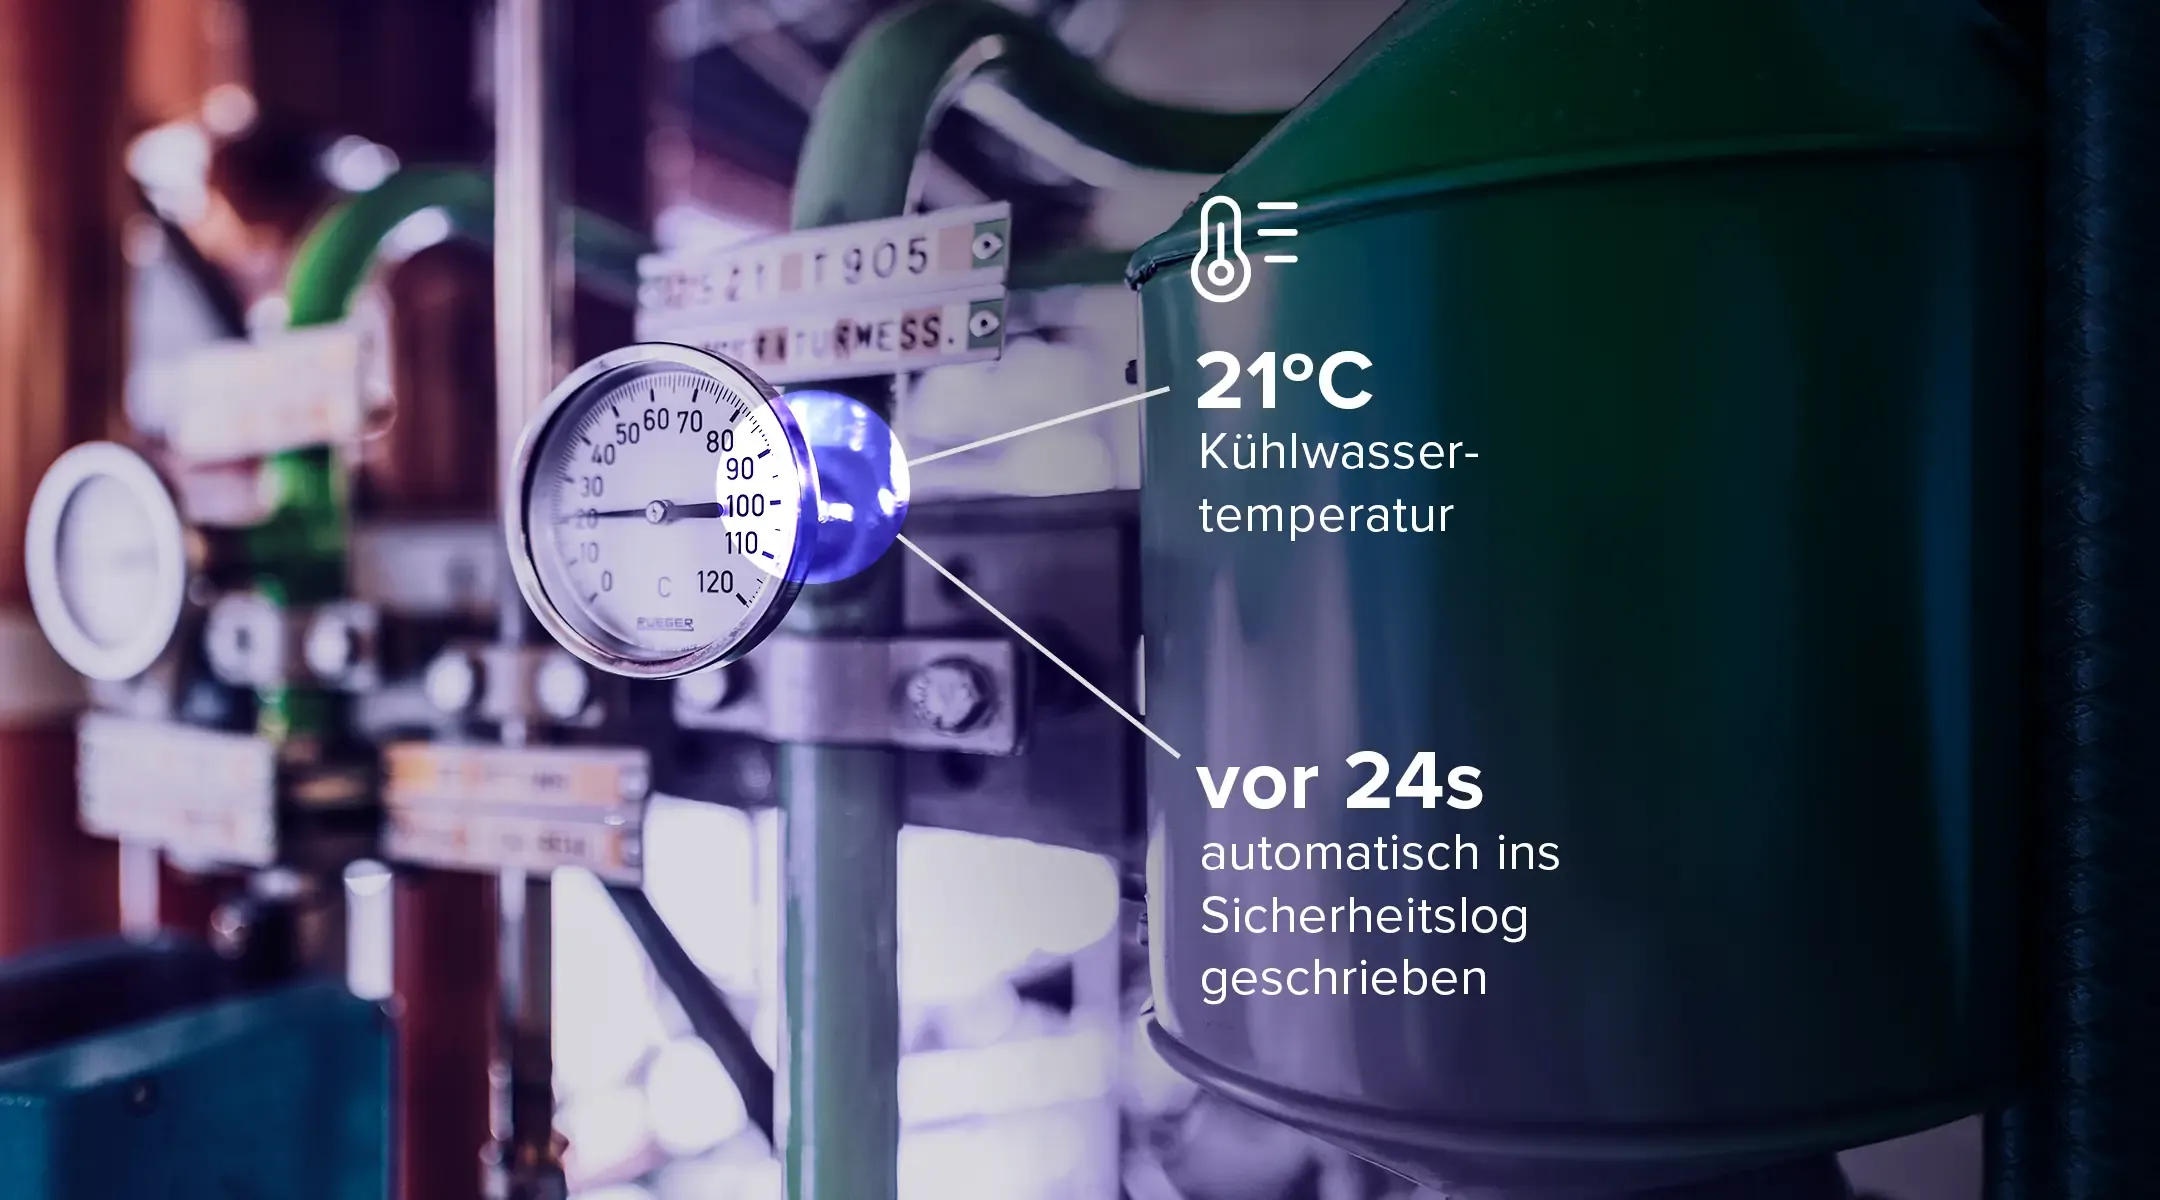
Security must not only be implemented but also monitored. Monitoring, logging, and alerting are therefore essential components of secure IoT operation.
Patch and lifecycle management
IoT components must be maintained and updated regularly. Without structured lifecycle and vulnerability management, security gaps emerge over time that can jeopardize operations.
How security by design relates to compliance
Security by design supports not only technical security but also regulatory and organizational requirements. This is particularly relevant in the context of NIS2, KRITIS, and ISO/IEC 27001.
NIS2 and operational resilience
The NIS2 Directive raises the requirements for cyber resilience, risk management, and reporting processes. IoT solutions must therefore be designed to fit into existing security and governance structures.
KRITIS and high protection requirements
Critical infrastructures are subject to elevated security requirements. IoT systems must be planned and operated with particular care there in order to ensure the confidentiality, integrity, and availability of plants and their information.
ISO/IEC 27001 and security management
Systematic information security management requires clear processes, roles, and controls. Security by design makes it easier to embed IoT solutions into an existing ISMS.
The role of the IoT System House
An IoT System House can only implement security by design credibly if it understands security not as an add-on service but as part of the overall concept. This applies to architecture, connectivity, data center, operation, and support.
The systems integrator can:
- identify security requirements early,
- integrate technical protection measures into the architecture,
- organize secure operation,
- take compliance requirements into account,
- and clearly define security responsibilities together with the customer.
Security as part of the operating model
Secure operation does not end at go-live. It must be continuously monitored, maintained, and adapted to new risks - a continuous improvement process. This is precisely where the strength of an IoT System House with operational responsibility lies.
Questions companies should clarify in advance
Before an IoT solution is implemented, companies should answer the following questions:
- Which data and processes are especially worth protecting?
- Which security requirements apply to the project?
- Which systems must be separated from one another?
- Who is responsible for operation and monitoring?
- Which compliance requirements are relevant?
- How are updates, patches, and incidents handled?
- How can the solution be documented in an auditable way?
- What points of contact and effects does the IoT solution have on other operational areas?
- Which suppliers are affected by the IoT solution?
The more clearly these questions are answered, the more robust the security architecture will be.
Conclusion
In the Industrial IoT, security by design is not an option but a necessity. The more companies connect their plants, data, and processes, the more important a security architecture and security culture becomes that is factored in from the very beginning. This is the only way to permanently ensure confidentiality, integrity, and availability as well as compliance.
An IoT System House that consistently implements security by design thus creates the foundation for resilient, scalable, and auditable IoT solutions.
Continue reading here
The article "Cyber Resilience, NIS2 and ISO/IEC 27001 in IoT Operations" explores the regulatory and organizational perspective of IoT security in greater depth.